WE BREAK CHIPS
TO MAKE THEM UNBREAKABLE
Independent lab for side-channel analysis, fault injection, firmware reverse engineering and secure silicon. We test secure elements, TPMs, automotive MCUs, IoT, crypto wallets and industrial controllers — down to transistors.

About HWSEC.NET
We are engineers, not slideware. Oscillosopes, lasers, FIBs and decapsulation baths — not just checklists.

Our mission
HWSEC.NET was founded to close the gap between software security hype and silicon reality. A buffer overflow is patchable. A ROM mask bug, a leaky regulator or a clonable secure element costs millions. We find those flaws before attackers do — with invasive, semi-invasive and non-invasive techniques.
We work with chip vendors, automotive Tier-1s, crypto wallet makers, medical and industrial OEMs, plus red teams who need ground truth about hardware trust anchors.
Invasive & EMFI
Decapsulation, microprobing, laser fault injection, electromagnetic glitching, power analysis up to 20GS/s.
Firmware & crypto
Bootloader reversing, JTAG/SWD/UART extraction, custom crypto review, DPA/CPA, template attacks.
* on unprotected AES implementations under lab conditions. Protected targets vary — that's why you test.
Research Vectors
Six core practices. One goal: prove what happens when physics meets cryptography.
01 / Side-Channel Attacks
Power, EM, acoustic and timing analysis. CPA, DPA, MIA, deep-learning SCA against AES, RSA, ECC, Kyber.
ChipWhisperer20GS/s scopeLanger probes
02 / Fault Injection
Voltage, clock, EM and laser glitching to bypass secure boot, readout protection and PIN checks.
EMFILaserVCC glitch
03 / Firmware Reversing
Extraction via debug ports, flash dumping, bootloader vulnerabilities, Ghidra + custom loaders for exotic cores.
GhidraJTAGSPI dump
04 / Secure Element Audit
Common Criteria style testing of SE, TPM 2.0, eSIM, smartcards: logical + physical, anti-tear, anti-clone.
TPMJavaCardeSE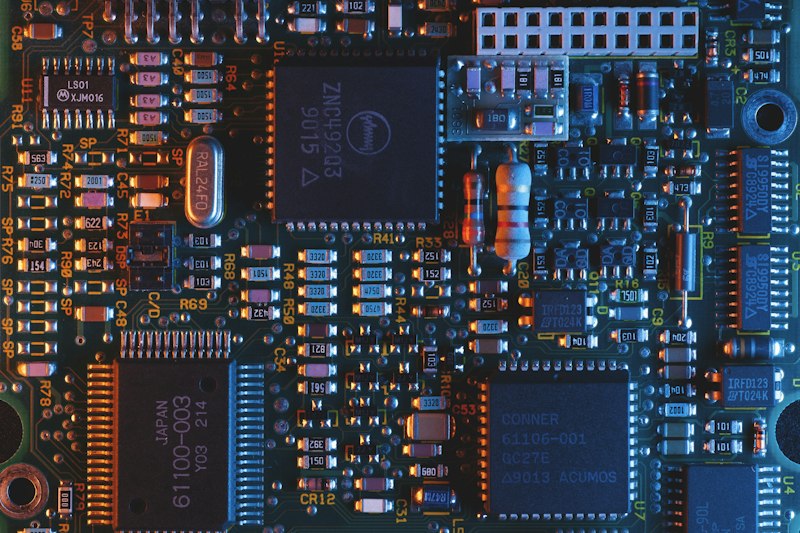
05 / PCB Forensics
Counterfeit detection, X-ray, delayering, netlist recovery, implant / trojan hunting, BOM integrity.
X-raySEMNetlist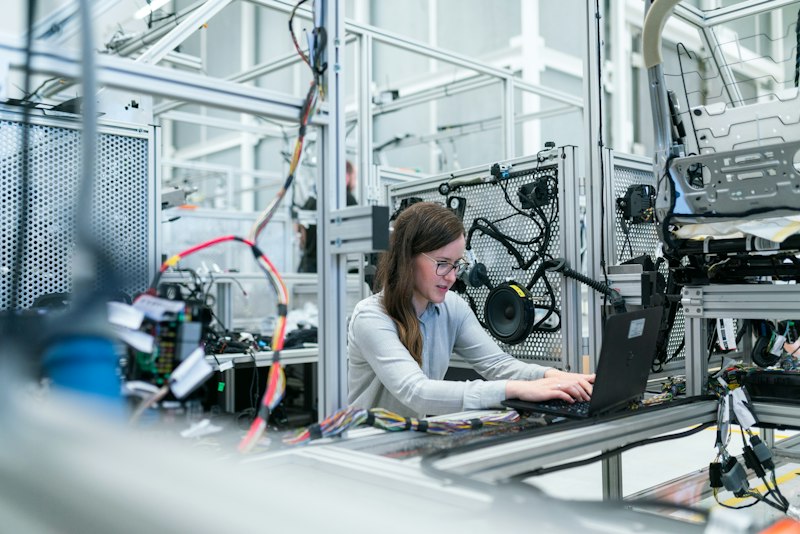
06 / Secure Design
Threat modeling, schematic review, PUF integration, anti-tamper meshes, secure provisioning for factories.
Threat modelPUFProvisioningThe Lab
15 benches. Faraday cage. Failure is data — every glitch is logged.
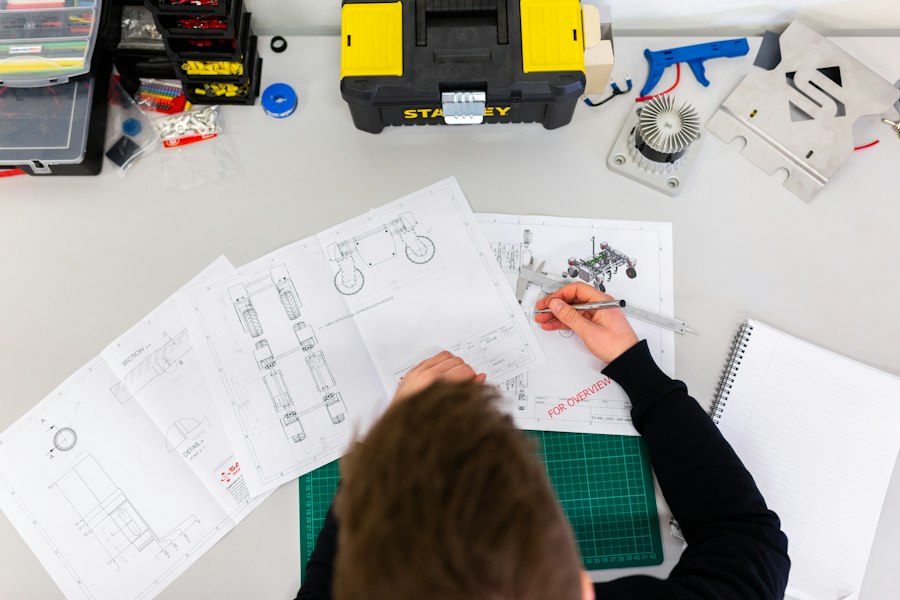
SCA BENCH — 20GS/s
Keysight + Riscure + custom amplifiers. 14k traces to full AES break on unprotected Cortex-M.
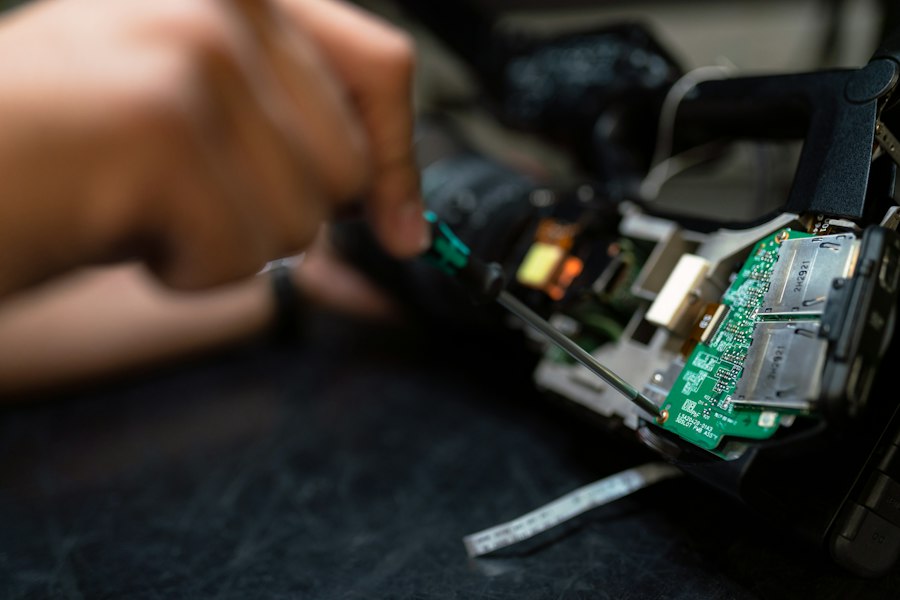
EMFI / LASER CELL
DTS + ALPhANOV laser. 5μm spot, RDP bypass on STM32, nRF, SAM L11.

DECAp + MICROPROBING
Fuming nitric, plasma etch, FIB edits, needle probing of ROM buses.
REVERSING FARM
40TB firmware corpus, JTAGulator fleet, Ghidra headless + ML-assisted triage.
Attack Method
01 — Recon & Teardown
X-ray, PCB mapping, BOM analysis, debug port discovery, threat model. 3–5 days. You get a full hardware BoM + attack surface map.
02 — Non-invasive
UART/SWD/JTAG, firmware dump, bootloader fuzzing, power/EM capture. No damage, maximum signal.
03 — Semi-invasive
Voltage/clock/EM glitching, RDP downgrade, option byte attacks, crypto SCA with 10k–1M traces.
04 — Invasive
Decap, laser, microprobing, ROM extraction. For high-assurance targets and counterfeit proof.
05 — Report & Fix
Reproducible PoCs, video, CVSS-HW scoring, schematic-level fixes, retest included. No 200-page PDF fluff.
Latest News
Disclosures, teardowns, tooling and lab notes. Click any card to open full analysis.
Hard Questions
What is HWSEC.NET exactly?
An independent hardware security lab. We do physical security testing: side-channel, fault injection, firmware extraction, PCB forensics and secure design review. Think pentest, but for silicon and boards.
How long does a hardware audit take?
Quick teardown: 1 week. Full black-box with glitching + SCA: 4–8 weeks. High-assurance with invasive work: 8–12 weeks. You get weekly demos, not silence.
Do you need source code / schematics?
No. We love black-box. If you have docs, we go faster and deeper — white-box lets us audit crypto implementations line-by-line and review schematics for anti-tamper gaps.
Will you destroy our devices?
Some will die heroically. Decap and laser are destructive by nature. We ask for 5–15 samples depending on target. Non-invasive phases are fully non-destructive.
Do you handle responsible disclosure?
Yes. 90-day coordinated disclosure by default, CVE assistance, vendor liaison, and retest after fix. We never sell zero-days.
Send us your hardest board
NDA in 24h. Teardown quote in 72h. Ship 5 samples — we handle the rest, from Faraday cage to final PoC video.
